 BTC
 ETH
 USDT
 BNB
 XRP
 USDC
 SOL
 TRX
 ZEC
 FIGR_HELOC
 HYPE
 DOGE
 LINK
 XMR
 WBT
 USDS
 ADA
 RAIN
 LEO
 XLM
 NEAR
 BCH
 UNI
 CC
 LTC
 SUI
 USDE
 AVAX
 DAI
 GRAM
 USD1
 HBAR
 QNT
 TAO
 SHIB
 BTW
 CRO
 USDG
 XAUT
 PYUSD
 ONDO
 ENA
 M
 OKB
 RLUSD
 USYC
 PUMP
 AAVE
 BUIDL
 USDY
 MNT
 DOT
 WLD
 ASTER
 SKY
 MORPHO
 WLFI
 PAXG
 PEPE
 ICP
 USDD
 ARB
 HTX
 ETC
 EURSAFO
 U
 USDGO
 BGB
 VVV
 USDF
 BFUSD
 KAS
 POL
 JUP
 GT
 LIT
 ALGO
 RENDER
 CAKE
 JST
 PI
 KCS
 ATOM
 BCAP
 FIL
 DASH
 NEXO
 AERO
 VET
 INJ
 USTB
 APT
 EUTBL
 STABLE
 GHO
 ETHFI
 AKE
 PYTH
 XDC
 PENGU
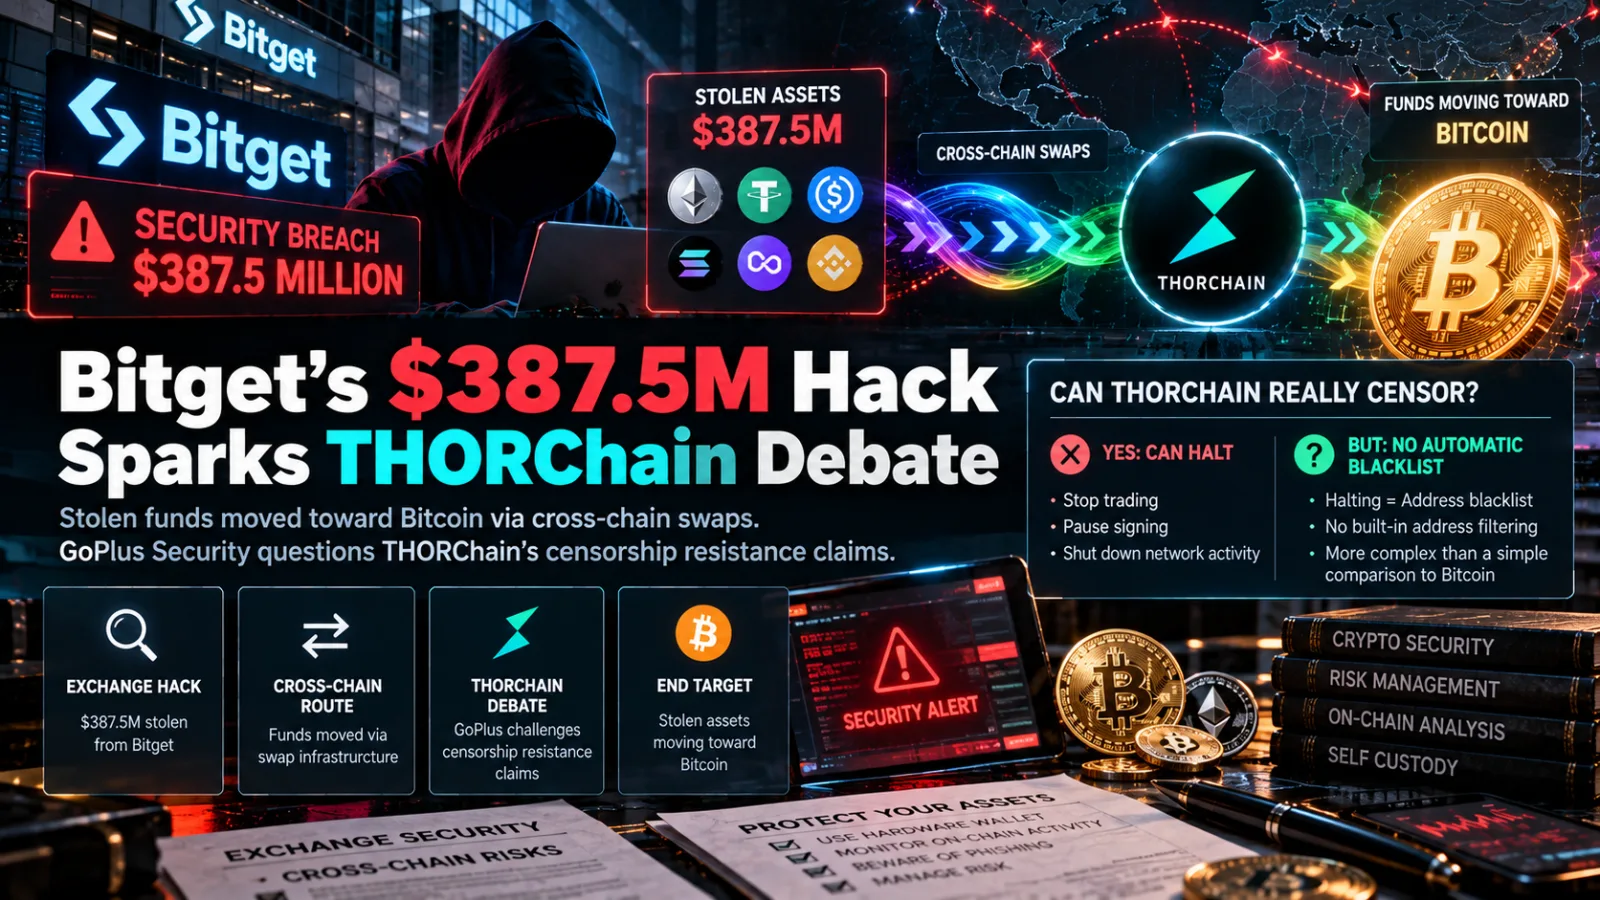
Bitget's $387.5 million security breach has become more than an exchange hack. After stolen assets began moving toward Bitcoin through cross chain swap infrastructure, GoPlus Security challenged THORChain's claim that it is comparable to censorship resistant networks such as Bitcoin. Yet the verified evidence is more complicated: THORChain can halt trading and signing, but that does not automatically give it a working address blacklist. The gap between those two facts is now the real story.
For practical risk controls, review AirdropHotList's crypto safety guide.
The XRP trail turned a custody failure into a protocol test
Bitget says attackers transferred approximately $387.5 million across the XRP Ledger, Ethereum and several EVM networks, Zcash and Tron on September 24. The exchange says the vulnerability has been identified and remediated, while Mandiant and SlowMist are supporting the investigation. Bitget has also published attacker addresses and offered a 5% bounty for eligible actions that freeze or recover affected assets.
XRP became the most visible part of the moving haul. A CoinDesk review of XRP Ledger records found that roughly 54 million XRP had left the original holding accounts by September 26, worth about $83 million at the price used in that report. An earlier Bitquery snapshot at 02:54 UTC recorded 27.63 million XRP moved onward and 75.35 million XRP remaining across six accounts. These are dated snapshots of a rapidly changing trail, not contradictory final totals.
The distinction between movement and liquidation matters. Transfers out of the first wallets do not prove that an equivalent amount was sold on an exchange. Bitquery traced some routes toward THORChain and Bitcoin, but it did not measure the net amount of XRP dumped into a spot order book. The immediate risk is therefore routing and conversion pressure, not a verified $83 million market sale.
TRM Labs traced stolen BNB, ETH and TRX through routes that reached THORChain and paid out Bitcoin. GoPlus later claimed that about 101.5 BTC linked to the incident had exited through THORChain and that 27.63 million XRP was moving toward BTC. Those figures remain GoPlus's analysis, not totals independently confirmed by Bitget or THORChain.
Before connecting a wallet or approving any transaction, slow down and verify the source. Our crypto safety guide explains how to avoid fake claim pages, phishing links, risky approvals, and common wallet mistakes.
THORChain's vault design makes the Bitcoin comparison difficult
THORChain responded that it is "decentralized and permissionless" like Bitcoin, Ethereum and BNB Chain, asking what responsibility those networks should bear when stolen assets pass through them. That defense is consistent with its long standing position that open infrastructure should not make discretionary decisions about who may transact.
GoPlus's counterargument focuses on architecture rather than ideology. Bitcoin miners order transactions involving coins controlled by users' keys. THORChain, by contrast, temporarily receives assets in shared vaults and relies on nodes to generate outbound signatures. THORChain's own technical documentation says Bifrost observes external chains, consensus requires 67% agreement and vault transactions use a threshold signature scheme requiring supermajority participation.
That does not make THORChain centrally controlled. No single node holds the complete vault key, validators must bond RUNE and authority is distributed across the active set. It does mean the protocol performs a different function from a base layer that merely confirms transactions initiated by users. THORChain's nodes collectively participate in producing the outbound transaction itself.
A halt button is not the same thing as a blacklist
GoPlus is correct that intervention tools exist. THORChain documents chain specific controls for halting signing, liquidity operations, trading and chain observation. Its security framework also allows a single node to pause trading for up to 720 blocks, with additional nodes able to extend the pause.
However, the published existence of emergency halts does not prove that validators can currently reject one flagged address while processing every other swap normally. Network pauses, chain wide signing halts and address level censorship are technically and politically different actions. THORChain's emergency documentation is primarily written for threats to protocol solvency and vault funds; it does not state that every external theft automatically requires a halt.
This is the weakness in both extreme arguments. THORChain cannot credibly present itself as having no intervention capacity, but critics cannot treat a blunt emergency stop as evidence of a precise, production ready blacklist. Building that capability would introduce an additional question: who maintains the list and what evidence threshold gives that party power over a permissionless protocol?
Not every reward campaign deserves your time. Before you commit, compare this opportunity with our active airdrops list and focus on campaigns with clearer upside, better trust signals, and realistic participation steps.
The May exploit established a precedent but not an answer
THORChain's own history explains why the criticism has traction. On May 15, 2026, an attacker exploited weaknesses in its GG20 threshold signing implementation and drained approximately $10.7 million from one vault. According to the protocol's official incident report, automatic solvency controls halted signing and trading across several chains before node operators coordinated a broader stop.
That response proved validators can coordinate when THORChain's own liquidity is threatened. It did not settle whether they should use the same powers when stolen assets from an outside exchange enter the protocol.
The investor paradox is unusually sharp: the controls that make THORChain safer during an exploit also weaken the cleanest version of its neutrality argument. Using them against flagged funds could reassure exchanges and compliance focused integrators while creating a censorship precedent. Refusing to use them protects permissionless operation but increases reputational and regulatory pressure whenever hackers choose THORChain as an exit.
XRP movement is not the same as XRP selling
For XRP holders, the critical variable is where the tokens land next. Transfers into fresh self custody accounts change the tracing picture but do not directly consume exchange bids. Deposits into centralized venues, swaps through deep liquidity routes or conversion into Bitcoin would create more measurable market consequences.
Bitget's recovery schedule is a separate source of XRP specific friction. The exchange scheduled BTC withdrawals for September 28, ETH for September 29 and USDT for September 30. XRP falls into the broader "other tokens" phase scheduled for October 2 at 08:00 UTC. Until the platform shows XRP withdrawals operating normally, customers face an exchange access issue alongside the unrelated movement of stolen coins.
Still unsure about wallets, eligibility, or reward rules? Visit our FAQ page for quick answers before joining any new crypto campaign.
RUNE now carries a governance question the market cannot ignore
For THORChain and RUNE, the key risk is not simply whether validators halt the network. It is whether the community can articulate a consistent boundary between protocol defense, sanctions screening and transaction neutrality.
A targeted intervention would demonstrate coordination and may disrupt legitimate volume alongside attacker routes. Continued inaction preserves the protocol's permissionless thesis, yet could push wallets, interfaces and centralized partners to add screening at their own layers. Either outcome changes how investors should evaluate THORChain: not just as cross chain liquidity, but as infrastructure whose validator discretion is now under public scrutiny.
 Kryvora Network
 Note Systems
 Nado
The investor watchlist
- Updated fund tracing: Transaction hashes confirming how much stolen XRP actually enters THORChain and exits as Bitcoin.
- Validator action: Any Mimir vote, signing halt or formal proposal for address level screening.
- Bitget access: Successful XRP withdrawal restoration on or after October 2, rather than the timetable alone.
- Recovery evidence: New freezes, exchange interceptions or an increase in the amount Bitget reports recovered.
Conclusion
The Bitget hack does not prove that THORChain is centralized, and THORChain's permissionless design does not erase the discretion embedded in its vault and emergency systems. What the incident has exposed is a spectrum: distributed custody, validator coordination and censorship resistance can coexist without being identical to Bitcoin's model.
The strongest thesis is therefore not that THORChain must block the funds. It is that the market now knows meaningful intervention tools exist and will judge how validators define the conditions for using them. That unanswered policy choice may matter longer than the stolen XRP's next transaction.


 Gaming Platforms
 Crypto Casinos
 Blockchain Bridges
 Staking & Restaking
 DEX Token Swapping
 Crypto Wallets